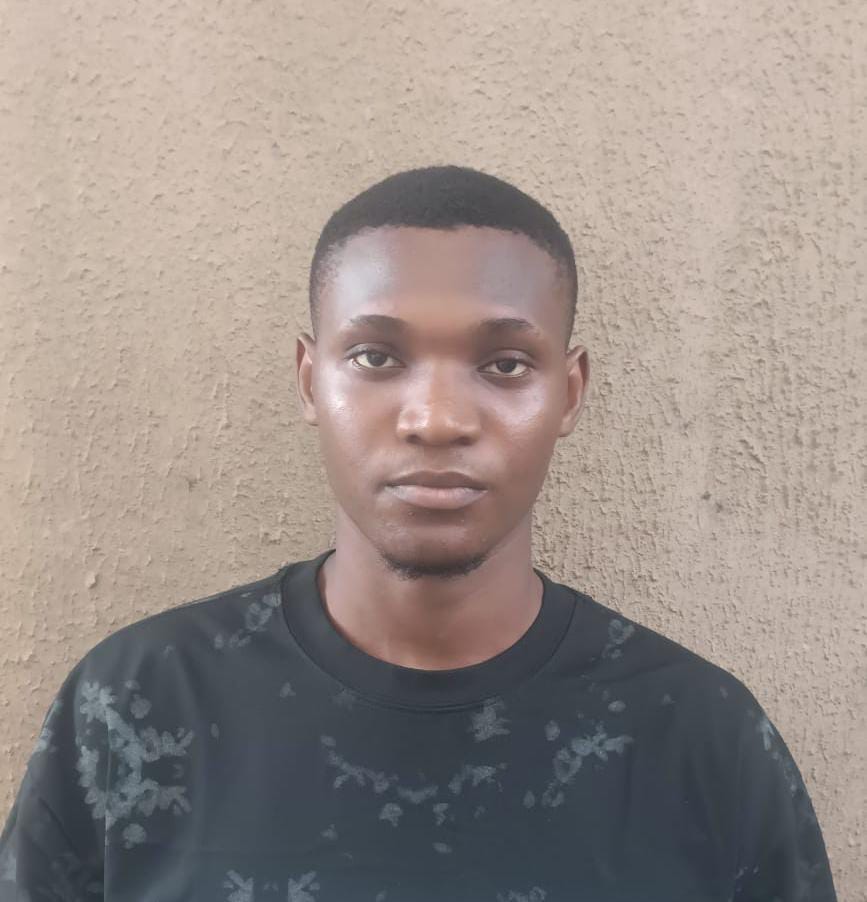
Charles Ebuka

CYBERSECURITY PROFESSIONAL

Charles Ebuka

SOC Analyst | Blue Team

Entry-level cybersecurity professional specialising in blue team operations, SOC analysis, threat detection and incident response. ISC2 CC Certified. Based in Lagos, Nigeria. Open to remote roles.

View Projects Contact Me Download CV

Technical Skills

SIEM & THREAT DETECTION

Splunk, SPL Query Writing, Log Analysis, Windows Event IDs, MITRE ATT&CK

NETWORK SECURITY

Wireshark, Nmap, Firewall Configuration, TCP/IP, DNS, HTTP, TLS, SSH

VULNERABILITY MANAGEMENT

Tenable Nessus, CVE Analysis, CVSS Scoring, Attack Surface Reduction

INCIDENT RESPONSE

BEC, Ransomware, DDoS Response, Playbook Development, Evidence Preservation

CRYPTOGRAPHY

AES-256, SHA-256, RSA-2048, OpenSSL, Digital Signatures, Hash Verification

OPERATING SYSTEMS

Linux (Ubuntu, Kali), Windows, Dual Boot Environment, Terminal Proficiency

Portfolio Projects

Splunk SIEM — BOTS v1 Investigation

Full SOC investigation reconstructing a web defacement attack chain using SPL across multiple log sources. Identified attacker TTPs, malware hashes and brute-force credentials.

Splunk SPL VirusTotal FortiGate
View on GitHub →

Vulnerability Management

Credentialed vulnerability assessment on Ubuntu 24.04 identifying 53 vulnerabilities including Critical CVSS 9.8 findings. Full identify → verify → remediate → re-verify workflow.

Nessus Nmap CVE Analysis Linux
View on GitHub →

Incident Response Playbook

Structured IR playbook covering BEC, Ransomware and DDoS scenarios with defined roles, communication strategies and MTTD/MTTR targets mapped to MITRE ATT&CK.

MITRE ATT&CK BEC Ransomware DDoS
View on GitHub →

FTP vs SFTP Security Analysis

Live Wireshark demonstration proving FTP exposes credentials in plaintext while SFTP encrypts all traffic through SSH. Configured FileZilla and OpenSSH environments.

Wireshark FTP SFTP Kali Linux
View on GitHub →

Network Setup and Security

Designed a secure office network with ACL firewall rules, Nmap port scanning and hardening. Captured and analysed HTTP, DNS, ICMP and TLS traffic using Wireshark.

Cisco Packet Tracer Nmap Wireshark Firewall
View on GitHub →

Applying Cryptography

Implemented AES-256, SHA-256 and RSA-2048 with digital signatures using OpenSSL on Kali Linux. Simulated real-world malware detection using hash verification.

AES-256 RSA-2048 SHA-256 OpenSSL
View on GitHub →

Wazuh SIEM Home Lab

Deployed Wazuh SIEM, monitored a Windows 10 endpoint, detected attacks in real time,and wrote custom detection rules mapped to MITRE ATT&CK.

Wazuh VirtualBox Windows 10 SIEM MITRE ATT&CK Linux
View on Github →
Certifications

🎓

TechCrush Cybersecurity Bootcamp

15-week intensive cybersecurity programme covering blue team operations, SOC analysis, network security and hands-on lab work.

Issued: June 2026

🛡️

ISC2 Certified in Cybersecurity (CC)

International cybersecurity certification covering security principles, network security, access controls and incident response.

Issued: July 2026

🌐

Cisco Introduction to Cybersecurity

Foundational cybersecurity certification covering cyber threats, network security, protecting personal data and devices, and security best practices.

Issued: August 2026

🛡️

Fortinet NSE 1 - Network Security Associate

Foundational knowledge of cybersecurity threats and the information security industry.

Issued: September 2026

🌐

Fortinentt NSE 2 - Network Security Associate

Understanding of network security products and how they protect against cyber threats.

Issued: September 2026

🎓

Fortinet NSE 3 - Network Security Associate

Knowledge of Fortinet's security portfolio and enterprises security solutions.

Issued: September 2026

Get In Touch

Open to remote SOC Analyst and blue team roles. Available for freelance cybersecurity work. Let's connect.